Configure Application Settings
Use this step to define application-level settings such as communication protocol, web server port, CORS origins, and security mode for the BigFix UI.
About this task
Procedure
- After completing the HTTPS certificates configuration, click Next button to open the Application Configurations screen.
-
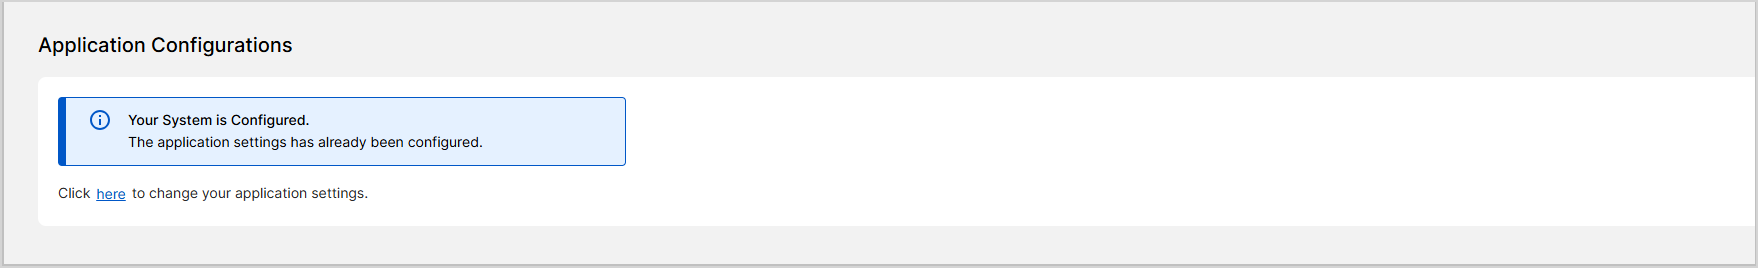
If the system detects existing application settings, a message is displayed
indicating that the application settings are already configured.
Click the provided link to change your application settings, if needed.
-
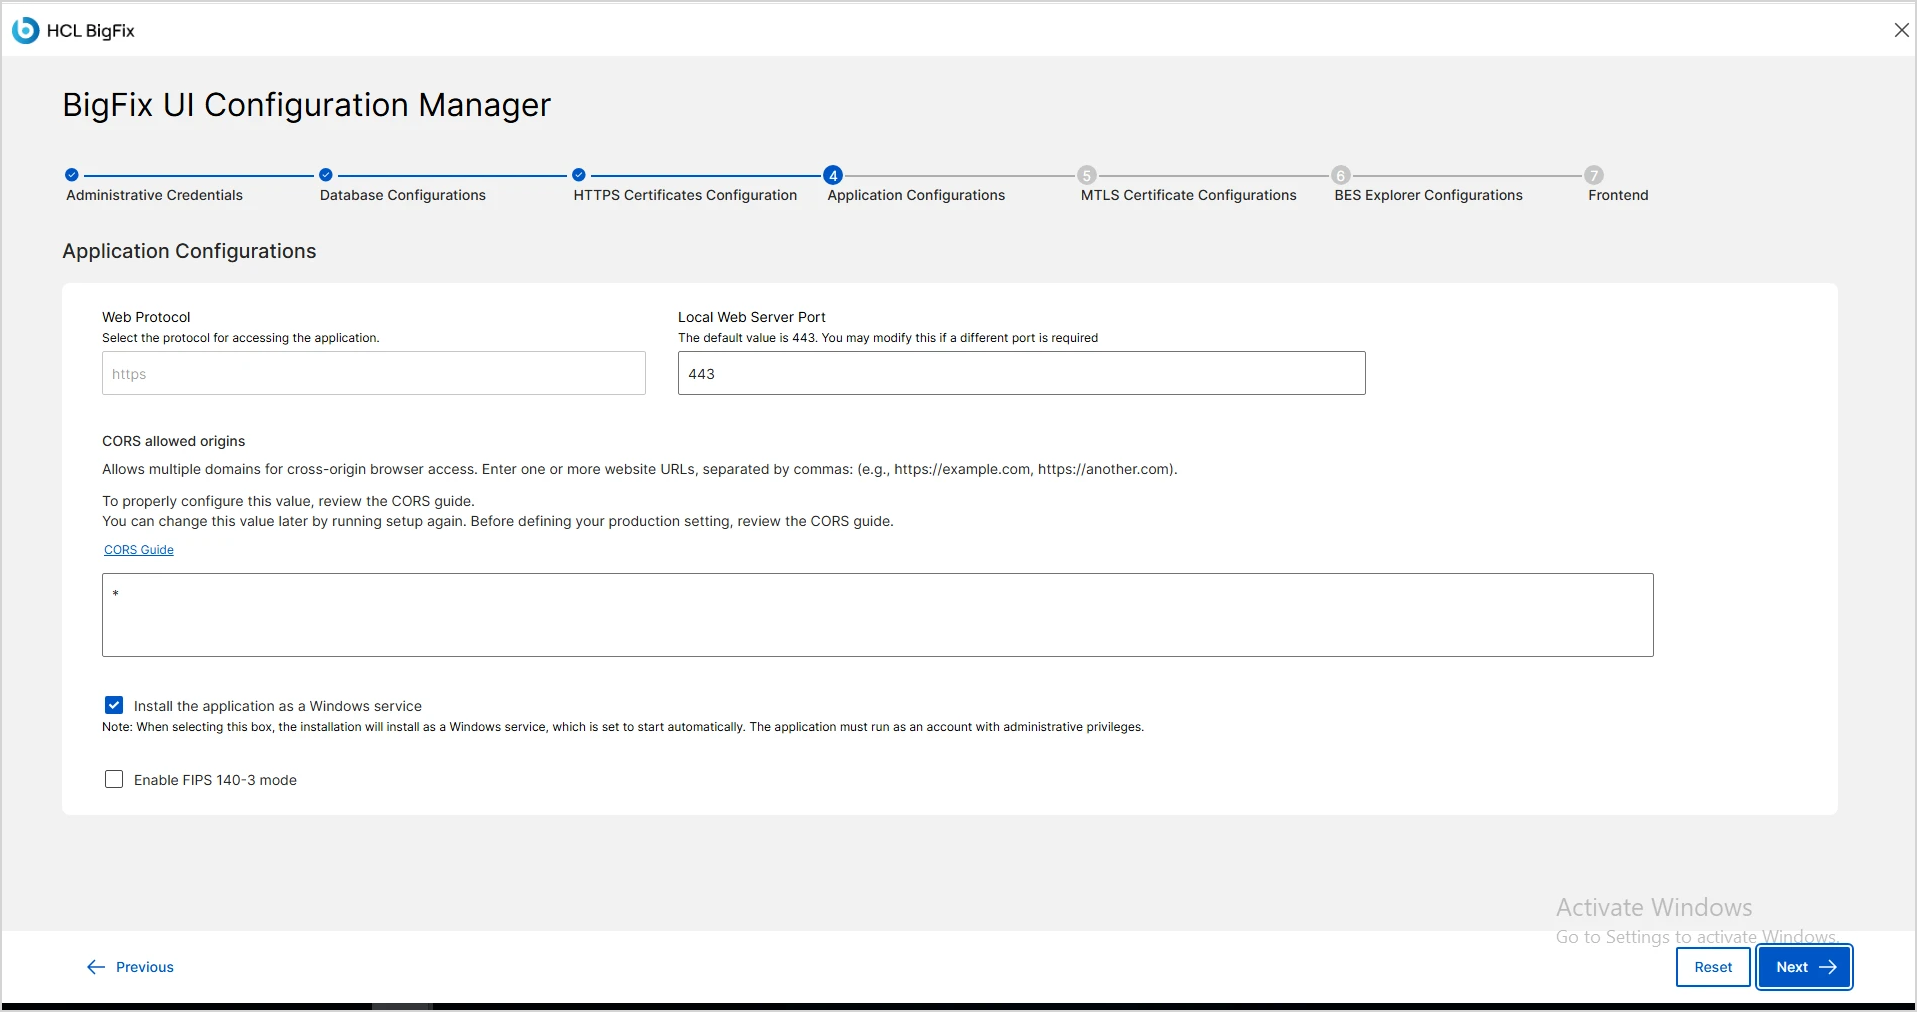
If no application settings exist, the Application
Configurations setup screen is displayed.
-
Review the Web Protocol field.
The field shows
httpsand is read-only. BigFix UI always uses HTTPS for access. -
In the Local Web Server Port field, review or enter a
port number.
- The default port is 443.
- You can provide a custom port if required.
-
In the CORS allowed origins field, enter the wildcard
*or one or more website URLs that are permitted to access this application.The field accepts one of the following values:
*— all origins are allowed. This is the default value.- A comma-separated list of origins, for example
https://192.168.0.7,https://bfui.myserver.com:8443.
Each origin in the list must follow these rules:
- The origin must start with
http://orhttps://. - The origin must not include a path, such as
/ui. - The origin must not end with a trailing slash.
- The list must not contain extra spaces or empty entries, such as
,,. - If an origin uses a port other than 443, the origin must include that port.
Important:By default, this field is set to*(all origins) to ensure access during initial setup. Use*for development only. In production, set a comma-separated list of trusted origins instead, according to your organization's security policy. For detailed guidance, see CORS allowed origins configuration.Note:The setup process uses this value to build the BigFix UI URL that it suggests when the setup finishes. For details, see How the suggested BigFix UI URL is built.To open the reference guidance for this field, click the CORS Guide link. You can change this value later by running the setup again.
-
Keep the Install the application as a Windows service
checkbox selected.
This checkbox is selected by default. When selected, the installation registers the application as a Windows service that starts automatically. The application must run under an account with administrative privileges.
Note:The setup requires administrative rights. If you run BFUI.exe as a non-administrator user, the setup stops with an error and does not open the Configuration Manager. Run the command prompt as an administrator. See Installation.Remember:Installing the application as a Windows service is recommended. Clear this checkbox only when you run the application manually from the command line, for example for development or debugging.Note:This checkbox will automatically disappear once the service is successfully installed. If the service is uninstalled, the checkbox will reappear. This behavior is intentional and is designed to reflect the current installation status of the service. -
Review the Enable FIPS 140-3 mode checkbox.
This checkbox is cleared by default. Select it only when your environment requires FIPS 140-3 compliant cryptography.
-
Review all settings and click Next to save the
configuration and proceed to the next step in the setup process.
If the CORS allowed origins field contains the wildcard value
*, the Confirm less restrictive CORS settings dialog appears. The dialog warns that a wildcard lets any domain make cross-origin requests to your environment.- Click Yes, confirm to proceed with the wildcard value.
- Click Cancel to return to the form and enter trusted domains.
If you enter specific URLs in the CORS allowed origins field, this dialog does not appear.
If the application configuration is accepted, a success message is displayed.